April 8, 2026/
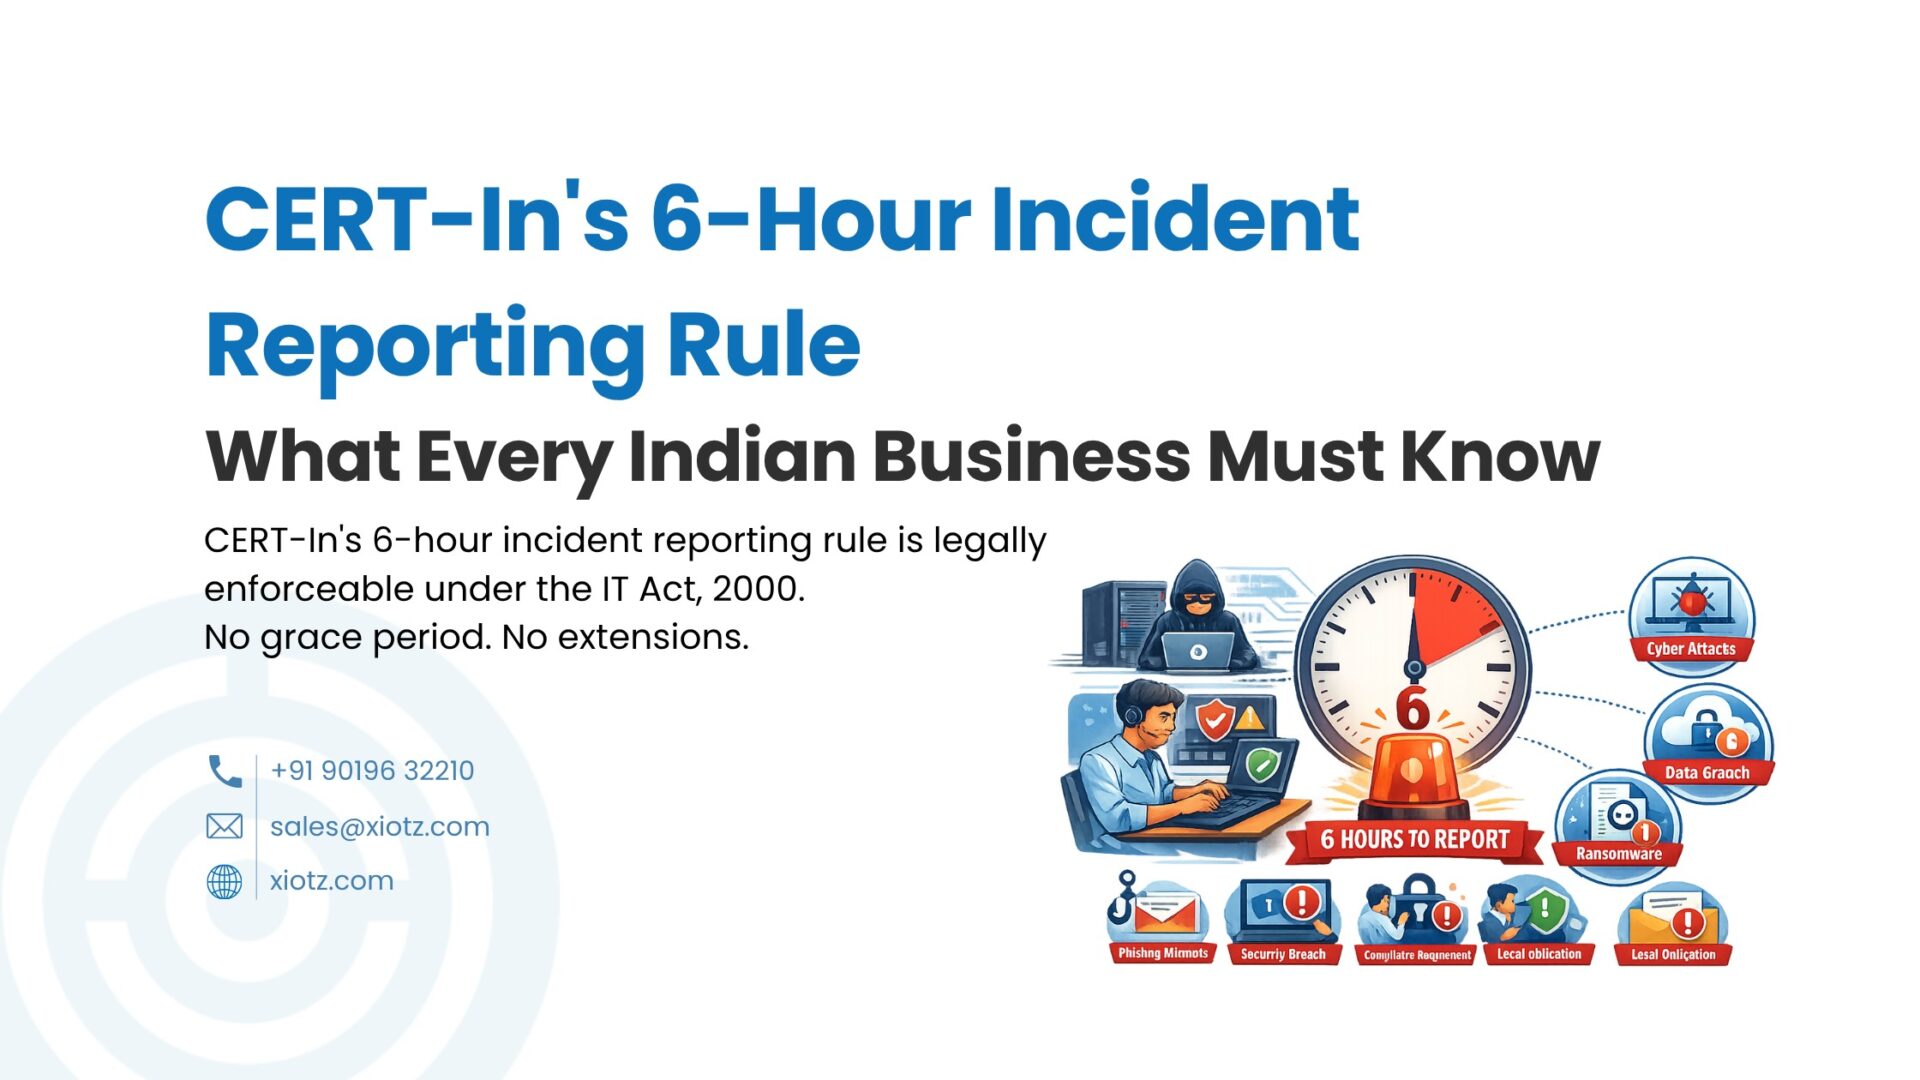
xIoTz helped shape India's CERT-In compliance framework. Here's the practitioner's checklist — all 15 controls, the penalties most businesses don't know about, and how to...



xloTz NIDS monitor network traffic in real-time, quickly detect and respond to security threats.

xloTz NIDS monitor network traffic in real-time, quickly detect and respond to security threats.

To identify weird patterns, abnormal activity & deviation in network behavior.

NIDS capture and analyze network packets in real-time to identify sources of network traffic and detect suspicious activity.

NIDS continuously monitor and analyze network packets in real-time to pinpoint sources of network traffic and identify any suspicious activity.
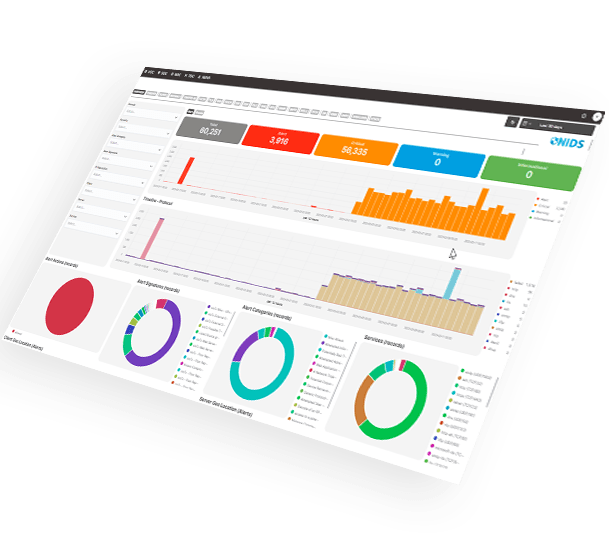
Provides deeper insights into network activity, empowering security teams to proactively identify sophisticated threats that may circumvent traditional security measures.

Blocks malicious traffic at the network perimeter, safeguarding critical systems and sensitive data from infiltration attempts.
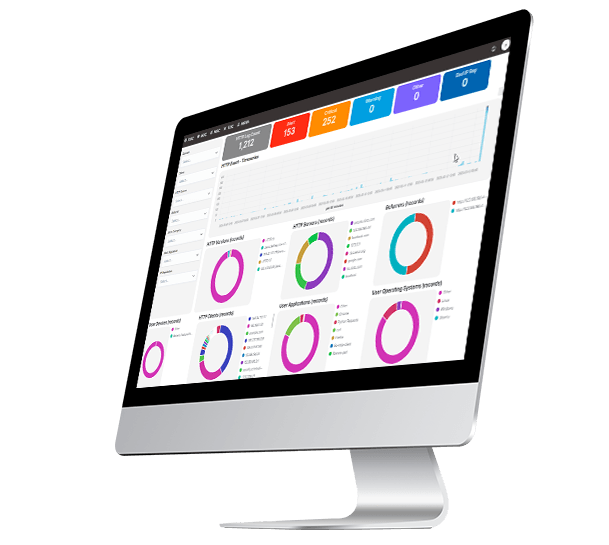
Streamlines the process of identifying and containing security incidents, allowing for faster resolution and reduced downtime.

Simplifies threat detection and analysis, freeing up valuable time for security teams to focus on high-priority tasks and strategic initiatives.

Facilitates adherence to industry regulations and data security standards that mandate network intrusion detection capabilities.

Provides confidence by ensuring your network is continuously monitored and protected by a robust intrusion detection system, allowing you to focus on your core business objectives.

Detects and responds to
network threats in real-time, quickly identifies and contains potential security breaches.

Greater visibility into enterprise networks, identifying potential security weaknesses, vulnerabilities & threats.

Proactive measures to prevent and mitigate the impact of the attack by Providing early warning of potential cyber threat.

Automated detection & response to security threats, reduce response times & minimize the impact of security incidents.

Customized to meet organization specific security needs & tailored security policies addressing unique requirements.

Provide regulatory compliances & industry requirements mandated by HIPAA, PCI-DSS standards.

Continuous monitoring and threat detection, to prevent costly security breaches & improves organization security posture.

Investigate past security
incidents, identify the source of the attack and take proactive steps to prevent future incidents.

xIoTz helped shape India's CERT-In compliance framework. Here's the practitioner's checklist — all 15 controls, the penalties most businesses don't know about, and how to...
India's 63 million MSMEs finally have a cybersecurity baseline. xIoTz has contributed to the National Cybersecurity Framework for MSMEs — specifically the 15 Elemental Cyber...
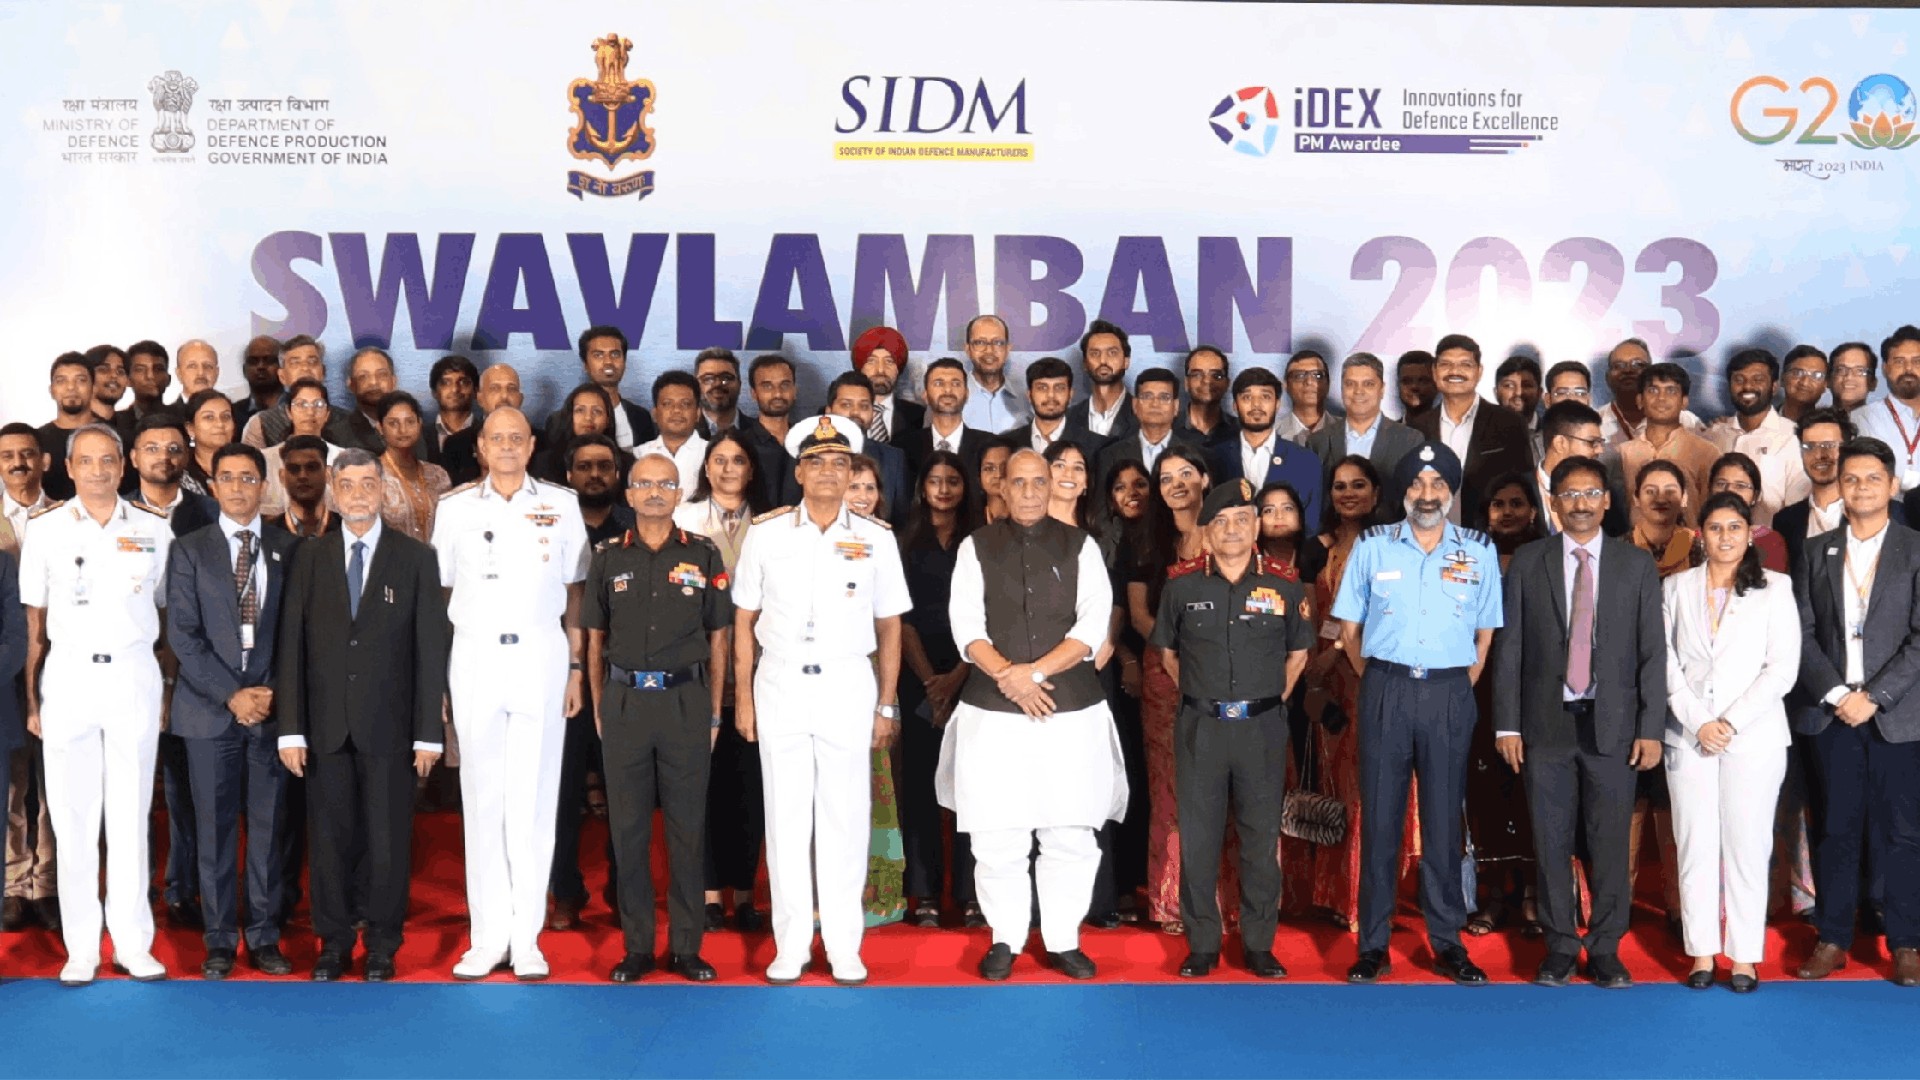
xIoTz Private Limited has been named the winner of a national defence innovation challenge for developing an indigenous Security Information and Event Management (SIEM) solution...

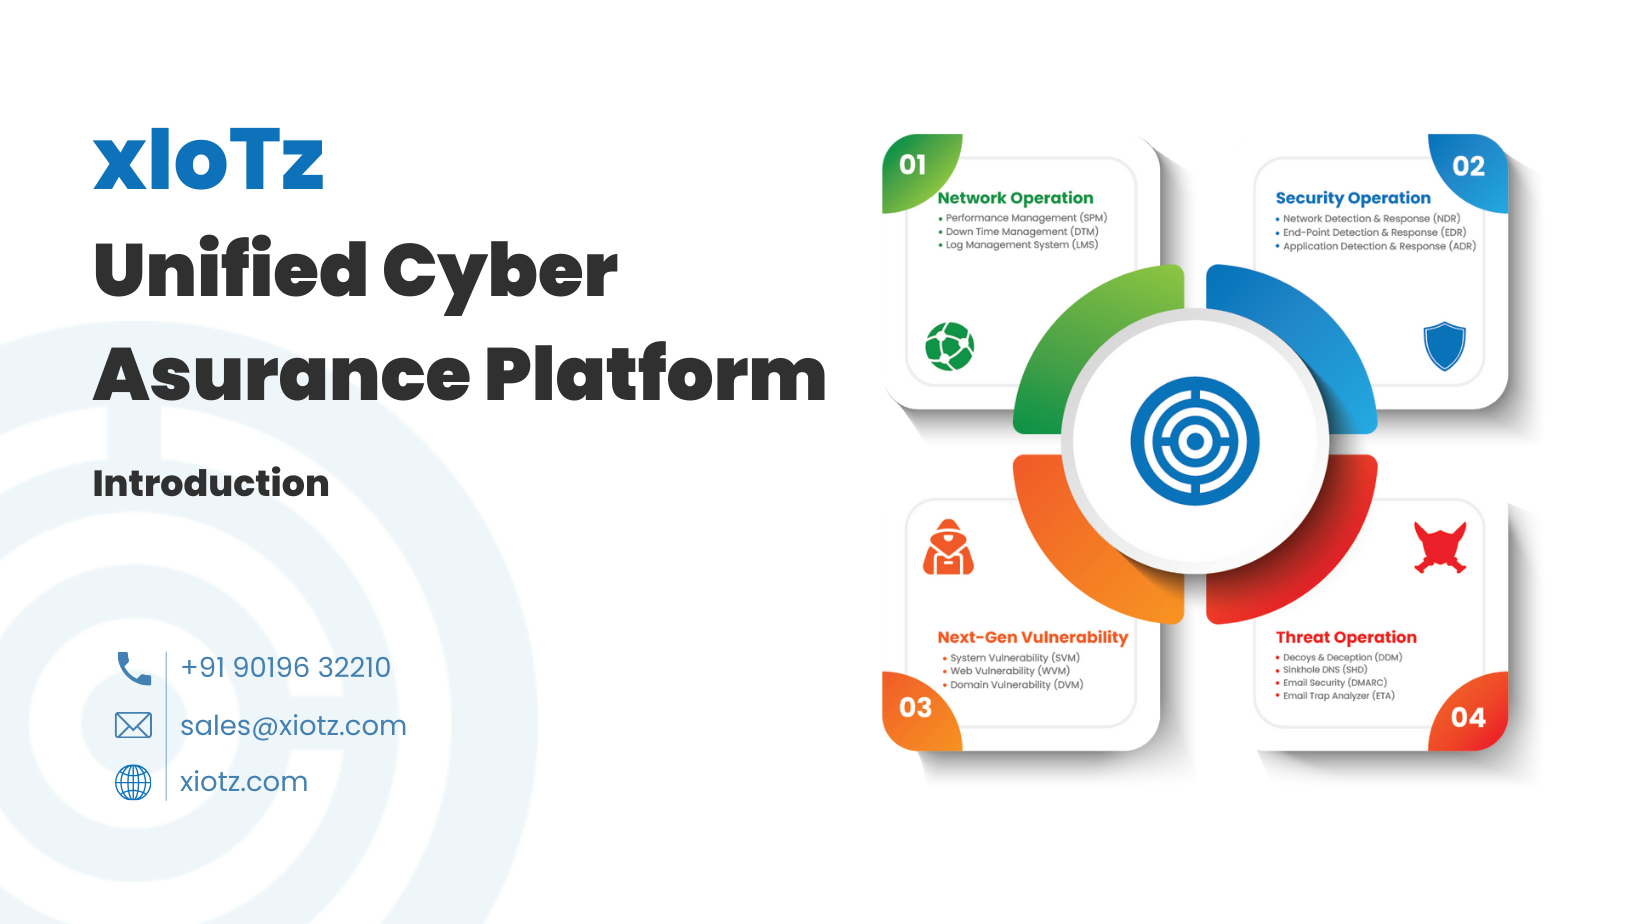
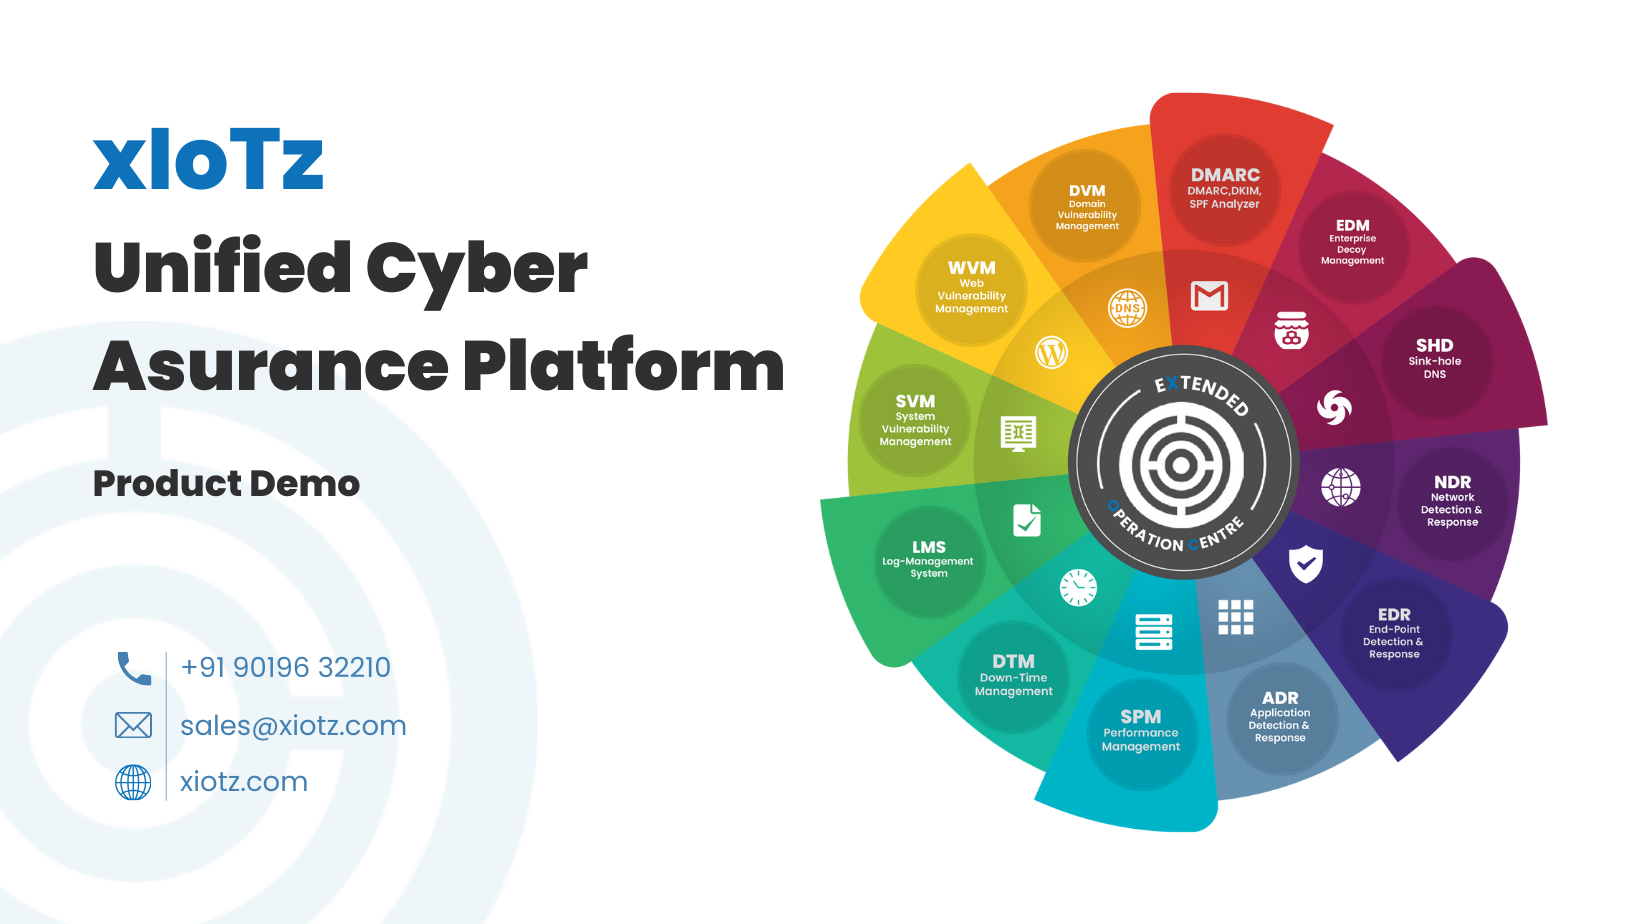
Network Detection and Response
End-Point Detection and Response
Application Detection and Response


System Vulnerability Management
Web Vulnerability Management
Domain Vulnerability Management