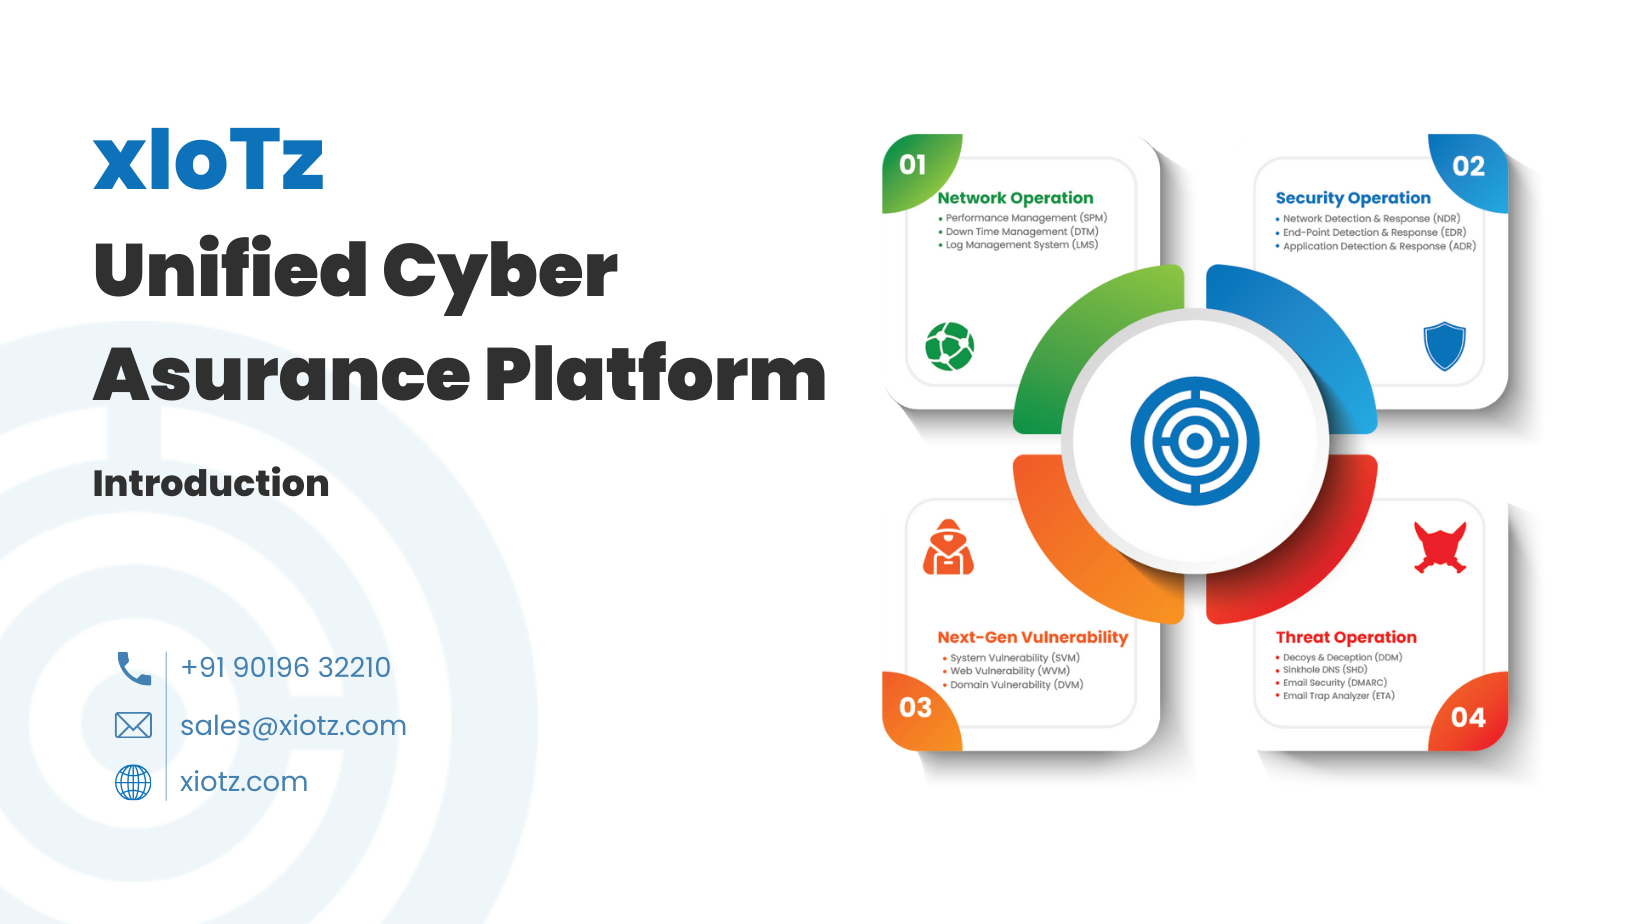
Proactive offensive security assessments conducted by ethical hackers to test, validate, and strengthen detection and response capabilities.
Real-time decoys and traps that expose attacker behavior early, helping stop threats before they spread across your network.
Advanced email analysis and detection layers that identify phishing, BEC attempts, and hidden threats to protect users and sensitive data.
Continuous monitoring of email and identity activity to detect impersonation and account takeover—prevent fraud and financial loss.
Real-time behavioral monitoring to detect and stop malicious activity across your infrastructure.
Email traps and deceptions that detect phishing, BEC, and hidden threats - protecting inboxes and sensitive data.
Real-time email and identity monitoring stop account takeovers, impersonation, and fraud before financial loss.
Built for enterprises xIoTz Decoys & Traps actively deceive attackers, delivering early threat detection, deep attack visibility, and enhanced cyber resilience—without disrupting production systems.
Built for modern enterprises, xIoTz Email Analyzer authenticates DMARC, DKIM, and SPF, detects phishing and spoofing, boosts deliverability, and preserves seamless communication and brand trust.
xIoTz BEC actively detects compromised mailboxes and impersonation attempts, delivering early fraud detection, deep visibility into email-based attacks, and rapid response—without disrupting business workflows.
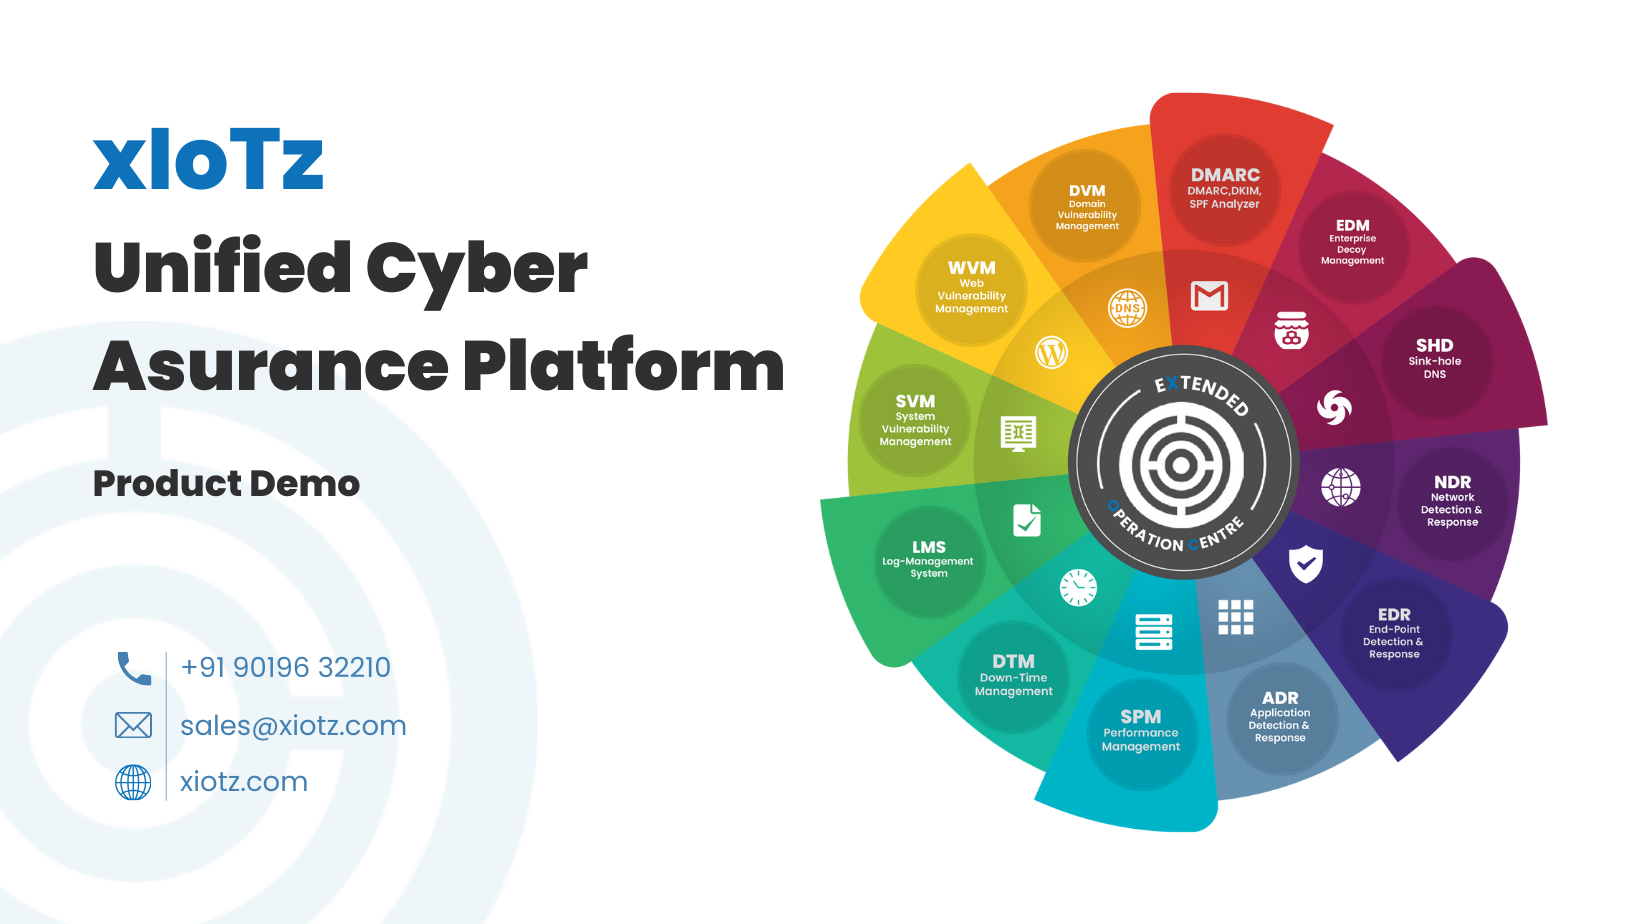
From real-time detection to rapid response, xIoTz TOC delivers the operational security capabilities modern enterprises rely on.
Combines global and local threat intelligence to enrich alerts, correlate events, and detect emerging threats early.
Hunts stealthy threats by analyzing attacker behavior, patterns, and indicators of compromise.
Automated response across tools and teams to contain threats, speed remediation, and minimize business impact.
Continuously assesses vulnerabilities and misconfigurations to prioritize the risks attackers are most likely to exploit.
Stops phishing, BEC, spoofing, and malware—protecting inboxes from the most common attack entry point.
Gives deep attacker visibility for faster investigations and more confident response.
Detects attacks on one system and triggers real-time, network-wide containment and response.
The xIoTz TOC delivers 24/7 visibility, intelligence-led detection, and rapid response—stopping threats before they impact uptime, data, or business continuity.
Yes. It detects active threats in real time, isolates compromised assets fast, and drives immediate containment to minimize disruption and damage.
It continuously monitors security posture and generates audit-ready reporting aligned to standards like ISO and CIS—making compliance easier and faster.
No. The xIoTz TOC strengthens your security operations without heavy hiring—providing expert monitoring, detection, and response support when you need it.
It detects impersonation, account takeover, and suspicious email behavior early—blocking phishing and BEC attempts before they trigger fraud or data loss.
One unified view across endpoints, networks, cloud, and apps—so your team can investigate faster, correlate smarter, and respond with confidence.
Experience xIoTz TOC - real-time detection, rapid response, and continuous protection across your enterprise.
Get Started with xIoTz TOCxIoTz UCAP is a self-healing military grade solution built on an Edge-Cloud platform providing 30+ Security Products built-in & integrated with SIEM enabling cyber safety & data assurance.
xIoTz Private Limited © 2026 | All Rights Reserved