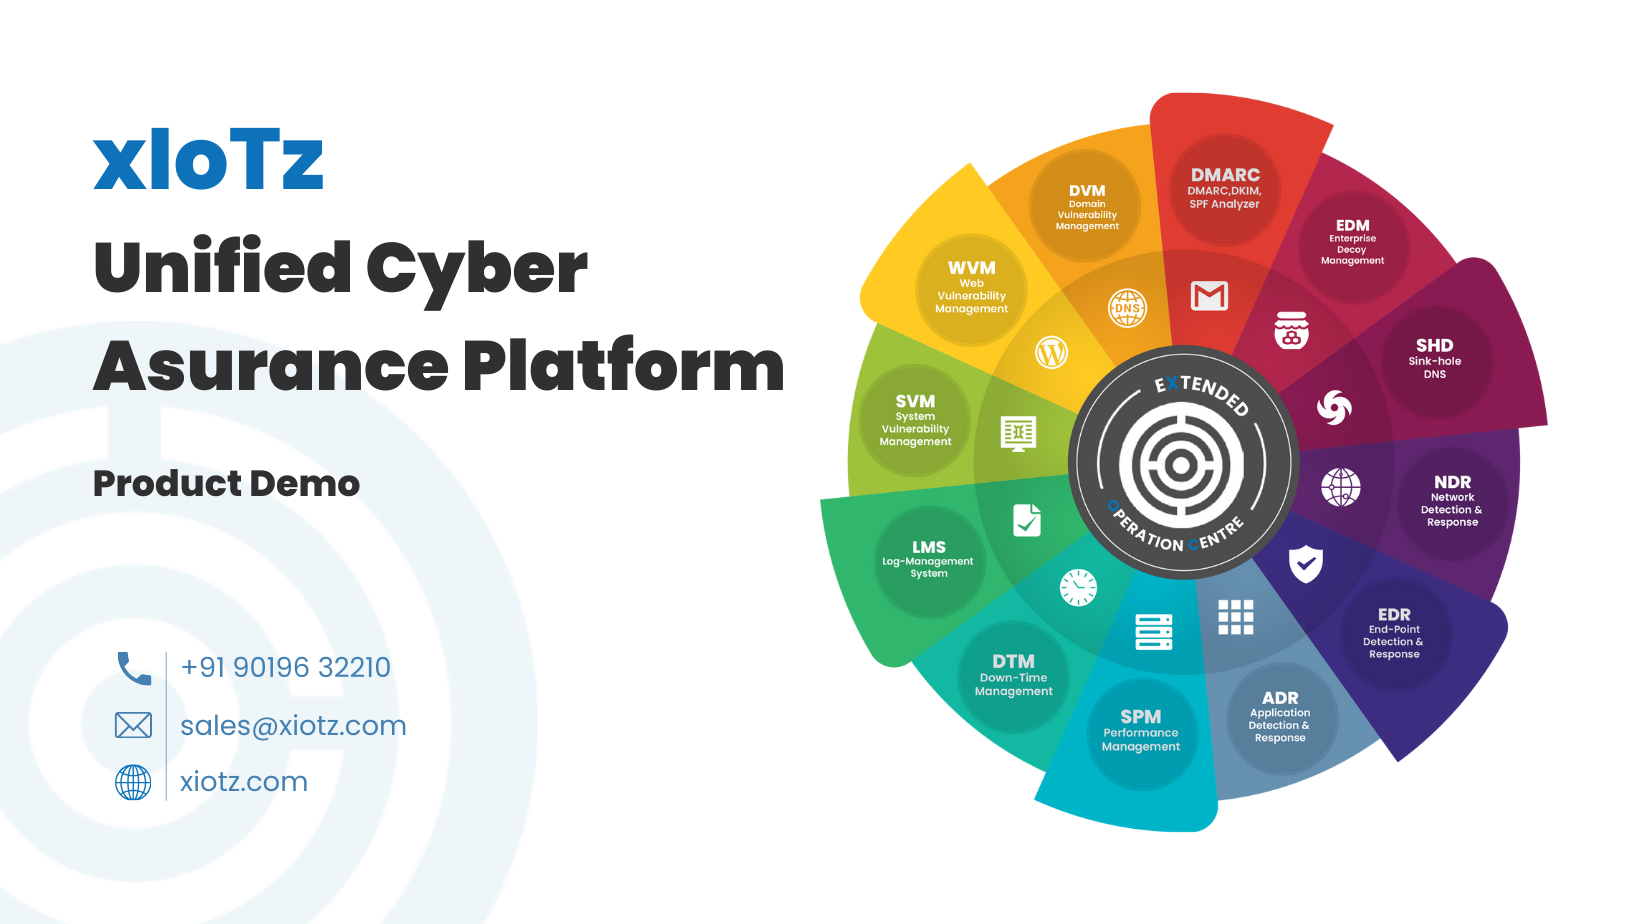
xIoTz | Unified Cyber Assurance Platform

xiotz SOC

Security
Operation Centre |

Defensive-Security to improve the organizations’s security posture by Collecting, Monitoring, Analyzing, Managing Data and identifying suspicious activity & alerts.

Secured Network

To identify and stop malicious attempts, our security solution uses behavior analysis, NIDS and continuous network traffic monitoring.

Secured System

Our solution uses CVE and CWE to prioritize vulnerabilities for proactive patching, and HIDS and EDR for continuous monitoring.

Secured App

Using an OWASP recommended practice and a Web Application Firewall (WAF), we strengthen your application.

OUR SECURITY COVERAGE

Complete Security for Your Entire Digital Environment.

Secured Network

End-to-end network visibility and control. Threats detected, isolated, and neutralized in real time.

Secured System

Critical systems continuously monitored and hardened. Unauthorized access and exploits blocked at the source.

Secured Application

Applications protected from vulnerabilities and misuse. Misconfigurations and threats identified before exploitation.

Automated Response

Threats handled automatically with predefined actions. Faster containment, minimal impact, zero manual delay

SECURED NETWORK

Network Detection and Response.

Built for Modern Enterprise, cloud and hybrid environments, xIoTz NDR enables faster response, reduced dwell time, and strengthen overall cyber resilience without disrupting network performance

Real - Time Threat Detection

Behaviour Based Analytics

Faster Incident Response

SECURED SYSTEM

End-Point Detection and Response.

Designed for Modern Enterprises, xIoTz EDR delivers endpoint visibility and rapid threat containment in real
time and remediate attacks, reducing response time and security risk without impacting performance.


Automated Threat Detection & Containment

Intelligent Endpoint Analytics

Orchestrated Endpoint Response

SECURED NETWORK

Network Detection and Response.

Built for Modern Enterprise, cloud and hybrid environments, xIoTz NDR enables faster response, reduced dwell time, and strengthen overall cyber resilience without disrupting network performance

Real - Time Threat Detection

Behaviour Based Analytics

Faster Incident Response

AUTOMATED RESPONSE

xIoTz Automated Response

Designed for Modern Enterprises, xIoTz EDR delivers
endpoint visibility and rapid threat containment in real
time and remediate attacks, reducing response time
and security risk without impacting performance.

Automated Threat Detection & Containment

Intelligent Endpoint Analytics

Orchestrated Endpoint Response

ADDITIONAL CAPABILITIES

Functions That Drive Next - Gen Cyber Protection.

From threat analytics to compliance automation, xIoTz SOC delivers the functions enterprises rely on

User & Entity Behaviour

Tracks normal user and system behavior.
Flags anomalies linked to misuse or compromise.

Automated Alerts & Reports

Triggers real-time security alerts.
Generates clear, audit-ready reports.

Vulnerabilities & Patching

Detects system and application vulnerabilities.
Helps prioritize and track patching.

Web Application Firewall

Protects applications from malicious traffic.
Blocks attacks without impacting users.

Compliance Monitoring

Monitors controls against regulations.
Simplifies audits and reporting.

Network Behaviour Anomaly

Detects unusual network activity.
Identifies hidden and lateral threats.

Network Flow Management

Visualizes data movement across networks.
Improves control and segmentation.

seminar animate

faq

xIoTz SOC - Your Questions, Answered

The xIoTz SOC continuously monitors networks, systems, applications, and cloud environments for suspicious activity, misconfigurations, and active threats—24×7.

Traditional SOCs rely on multiple disconnected tools. xIoTz SOC operates from a unified platform, correlating signals across environments to detect threats faster with fewer false alerts.

Yes. The SOC detects attacks in real time and initiates automated and guided responses to contain the incident, limit spread, and reduce business impact.

Yes. The SOC maintains centralized logs, alerts, and incident records that support regulatory requirements such as DPDP, ISO 27001, and industry-specific audits.

No. xIoTz SOC is designed to extend or replace in-house capabilities, providing expert monitoring and response without the cost and complexity of building a full SOC internally.

Unified security. Real outcomes. Continuous protection.

Experience xIoTz UCAP - bringing SOC, NOC, and compliance into one platform.

Get Started with xIoTz SOC

Services

xIoTz Unified Cyber Assurance platform

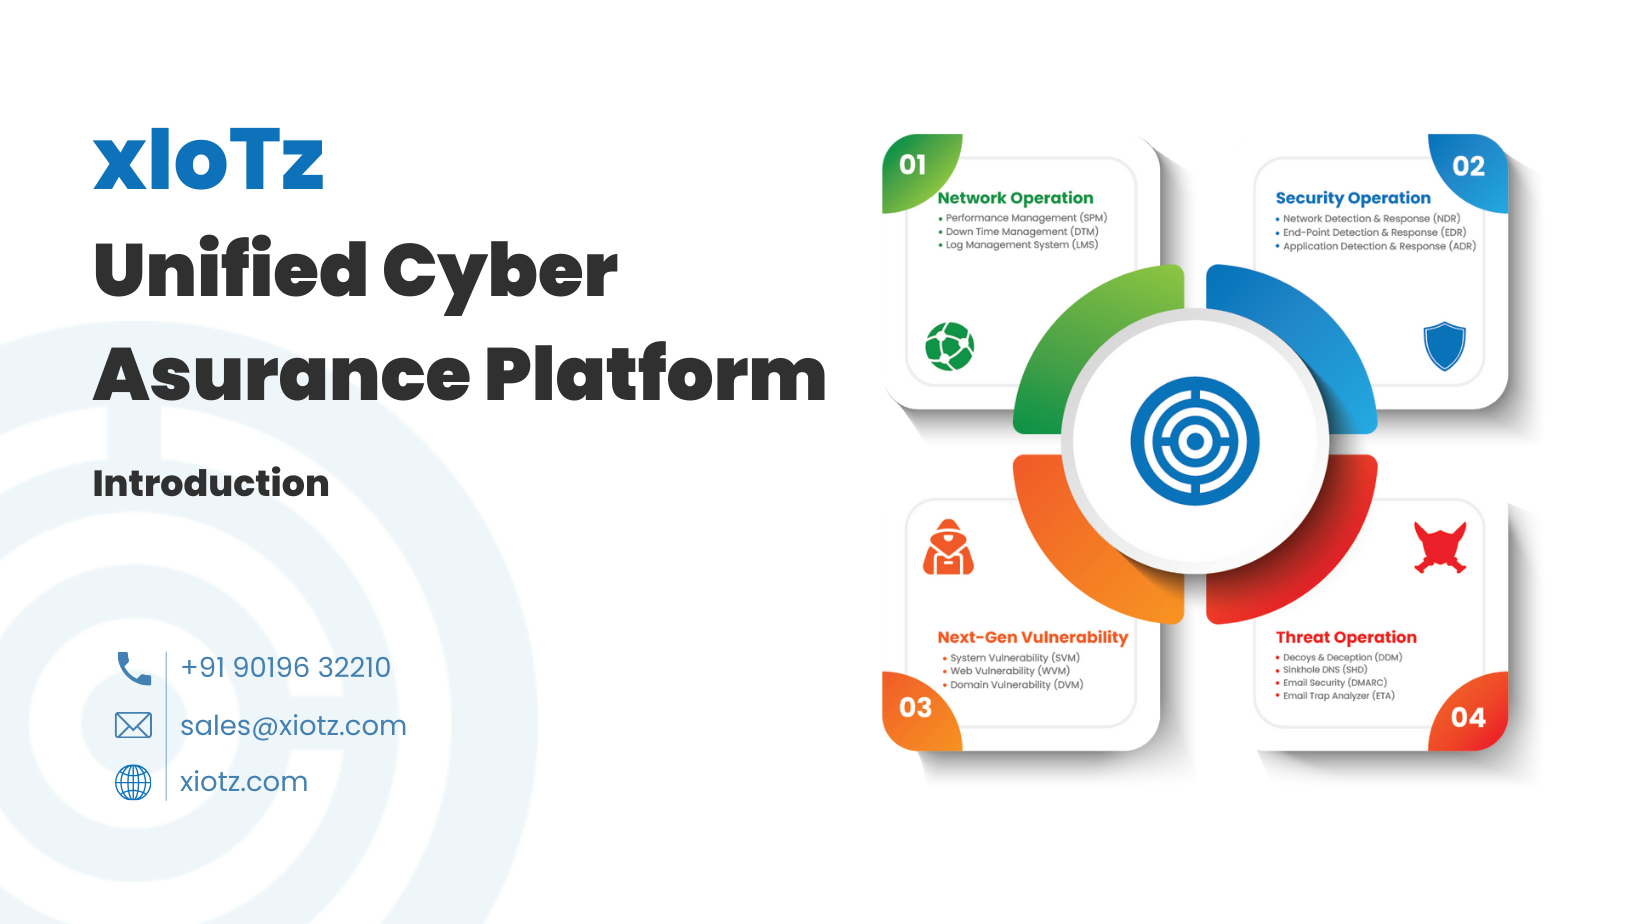
xIoTz UCAP is a self-healing military grade solution built on an Edge-Cloud platform providing  30+ Security Products built-in & integrated with SIEM enabling cyber safety & data assurance.

Security
Operation
Centre

SOC

Network
Operation
Centre

NOC

Threat
Operation
Centre

TOC

Cloud
Security Posture
Management

CSPM

Regulatory
Compliance
& Standards

RCS

Next-Gen
Vulnerability
Management

NGVM

AI-Intelligence
Operation
Center

XIOC
Free Demo Free VAPT Free VAPT