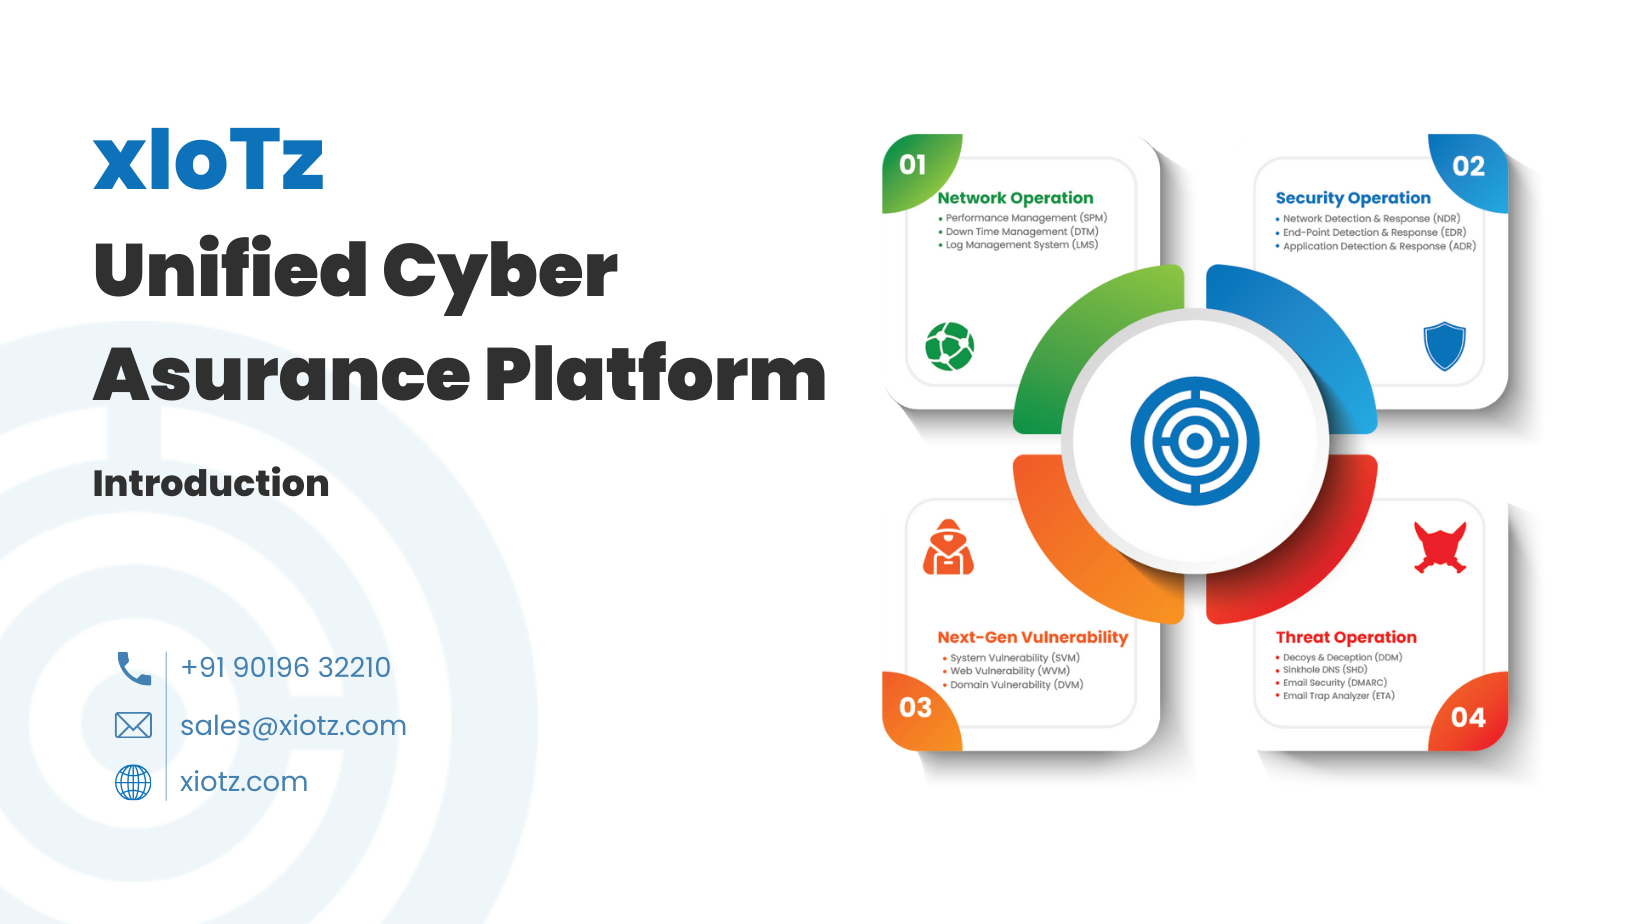
xIoTz | Unified Cyber Assurance Platform

CERT-IN ALIGNED CYBER CONTROLS FOR MSMES

15 Elemental Cyber Defense Controls
Simplified. Implemented. Continuously Assured. |

Compliance isn’t optional — but complexity is.

xIoTz Unified Cyber Assurance Platform transforms CERT-IN’s 15 Elemental Controls into measurable, business-ready protection — without the audit scramble.

Framework Architects

xIoTz contributed to shaping the structure of the 15 Elemental Cyber Defense Controls — giving us insight into how they should be implemented

Built to Implement

Our platform doesn’t just interpret controls — it operationalizes them with automation, visibility, and accountability

Always Audit-Ready

Real-time dashboards, control health scoring, and continuous monitoring ensure year-round compliance confidence.

CERT-IN MSME IMPLEMENTATION

Why Implementing CERT-In Controls Is Critical for MSMEs?

The 15 Elemental Cyber Defense Controls provide a structured foundation to protect revenue, reduce
regulatory exposure, and ensure long-term operational resilience.

Regulatory Exposure

Penalties under applicable IT Act provisions may extend up to ₹1 crore for serious non compliance.

Audit Risk

If controls aren’t operational, audit
findings can affect compliance standing and contract eligibility

Operational Impact

One breach can shut down operations, cost lakhs in recovery, and damage trust permanently.

CERT-IN MSME COMPLIANCE

The 15 Elemental Cyber Defense Controls

The framework centers around 15 Elemental Cyber Defense Controls specifically designed for smaller businesses

Effective Asset Management (EAM)

Establish and maintain an efficient asset management framework.
Network and Email Security (NES)

Safeguard networks systems against unauthorized access.
Network and Email Security (NES)

Safeguard email systems against unauthorized access.
Endpoint & Mobile Security (EMS)

Safeguard end-user devices by enforcing security policies and practices.
Secure
Configurations (SC)

Implement secure configuration of hardware and software.
Patch
Management (PM)

Systematically identifying, testing, and applying patches.
Incident
Management (IM)

Ensure timely detection, reporting, response to incidents.
Logging and
Monitoring (LM)

Continuous monitoring of systems, networks, and user activities
Vulnerability Audits and
Assessments (VAA)

Evaluate an organization’s security posture, policies.
Data Protection, Backup Recovery (DPBP)

To ensure the confidentiality, integrity, and availability of data.
Goverance and
Compliance (GC)

Ensure accountability and compliance with cybersecurity policies and regulations.
Robust Password
Policy (RPP)

Strengthen passwords to protect sensitive data from unauthorized access.
Access Control & Identity (ACIM)

Ensure that only authorized users and systems can access resources..
Awareness and
Training (AT)

Enhance cybersecurity posture by educating personnel on security policies.
Physical Security (PS)

Prevent unauthorized physical access to critical infrastructure, systems, and data.
Third - Party Risk
Management (TPRM)

Protect organization from security risks introduced by external service providers.
CERT-IN CYBER CONTROL EXECUTION

From Gaps to Enforced Cyber Controls

Delays increase exposure — our structured execution model turns regulatory mandates into measur
able protection and year-round readiness.

Gap
Assessment

  • Control mapping analysis
  • Risk scoring
  • Compliance maturity rating

Control
Implementation

  • Automated deployment templates
  • Policy enforcement
  • Technical hardening

Evidence
Generation

  • Audit-ready documentation
  • Log retention management
  • Incident response documentation

Continuous
Monitoring

  • Real-time alerts
  • Compliance dashboard
  • Ongoing posture scoring

IMPLEMENTATION PARTNER

Auditors Validate, We Implement

While independent auditors conduct assessments, our platform implements and enforces the 15 Elemental Controls — a framework we
contributed to shaping — ensuring safeguards are not merely documented, but actively applied and continuously monitored.

Capability Auditor xIoTz MSME UCAP
Primary Role
Independent assessment & reporting
Control design, deployment & enforcement
Engagement Model
Periodic (annual/engagement-based)
Continuous, year-round
Implements Controls
❌ No
✅ Yes – structured deployment
Technical Hardening
❌ Advisory only
✅ Direct configuration & automation
Continuous Monitoring
❌ Not ongoing
✅ 24×7 posture tracking
Evidence Collection
Manual validation
Automated evidence generation
Control Health Visibility
Limited to audit cycle
Real-time dashboards
Risk Scoring
Snapshot at assessment time
Dynamic compliance scoring
Remediation Ownership
Client responsibility
Guided & platform-driven execution
Framework Insight
Interpretation-based
Contributed to framework structure
Audit Readiness
Evaluates readiness
Enables readiness
Post-Audit Support
Limited
Continuous improvement cycle

STRATEGIC CYBER ASSURANCE

Who This Platform Is Built For?

Organizations that cannot afford regulatory penalties, contract loss, or downtime caused by weak control implementation.

Audit-Ready Organizations

For MSMEs that want structured implementation and year-round audit confidence — not last-minute compliance panic.

Implementation-Focused Businesses

For companies that need deployed, enforced, and measurable controls — not just advisory recommendations.

Regulated & High-Trust Ecosystems

MSMEs in government, enterprise, or regulated sectors where cybersecurity impacts eligibility and growth.

Growth-Driven Leadership Teams

For leaders who want enterprise-grade security and clarity—without the complexity.

xIoTz FAQ animate 03 1

FREQUENTLY ASKED QUESTIONS

Who This Platform Is Built For?

MSMEs operating in regulated or government-linked sectors are increasingly expected to implement mandated cybersecurity controls.

Serious violations under the IT Act may attract regulatory action and financial penalties, which can extend up to ₹1 crore.

No. Independent audits assess operational safeguards — not incomplete or inactive controls.

Delays increase regulatory exposure, breach risk, and potential contract loss.

No. Regulatory penalties, downtime, and recovery costs are often far higher than proactive control deployment.

Compliance Shouldn’t Be a Scramble. It Should Be Engineered.

Built by experts who helped shape the framework. Delivered as a platform that makes compliance measurable.

Book ConsultationDownload Compliance Readiness Guide

Services

xIoTz Unified Cyber Assurance platform

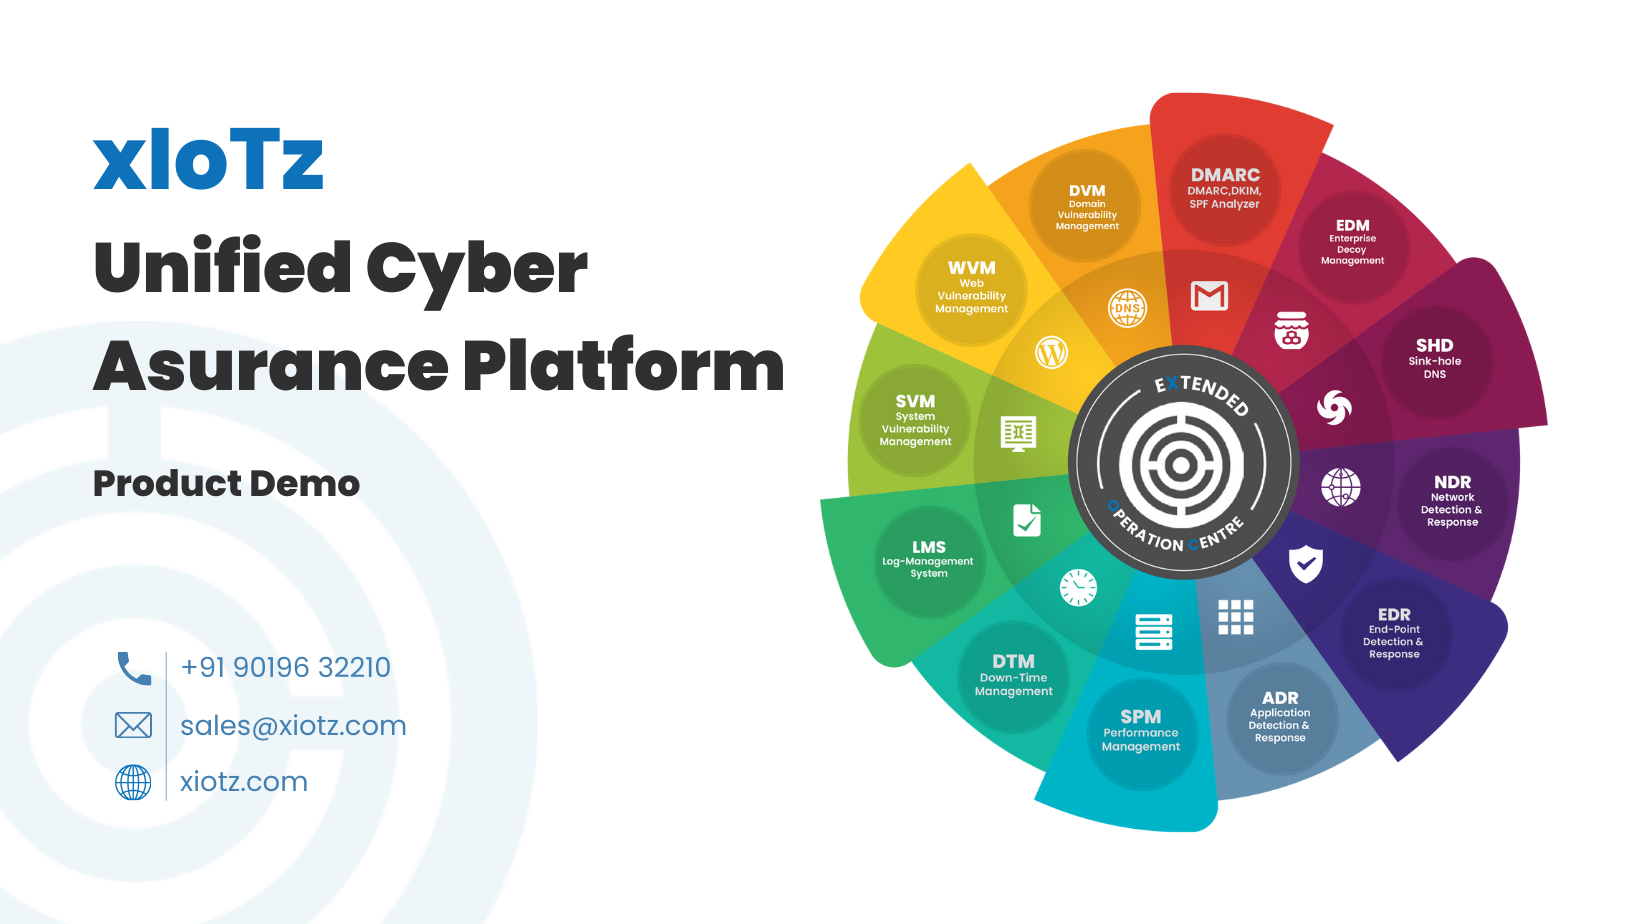
xIoTz UCAP is a self-healing military grade solution built on an Edge-Cloud platform providing  30+ Security Products built-in & integrated with SIEM enabling cyber safety & data assurance.

Security
Operation
Centre

SOC

Network
Operation
Centre

NOC

Threat
Operation
Centre

TOC

Cloud
Security Posture
Management

CSPM

Regulatory
Compliance
& Standards

RCS

Next-Gen
Vulnerability
Management

NGVM

AI-Intelligence
Operation
Center

XIOC

Blogs

Latest Posts & News

  • All Post
  • Awareness
  • Celebrations
  • Education
  • Event
  • Experience
  • Newsroom
  • Opportunities
  • Web Stories
  • xIoTz Features
Load More

End of Content.

Free Demo Free VAPT Free VAPT